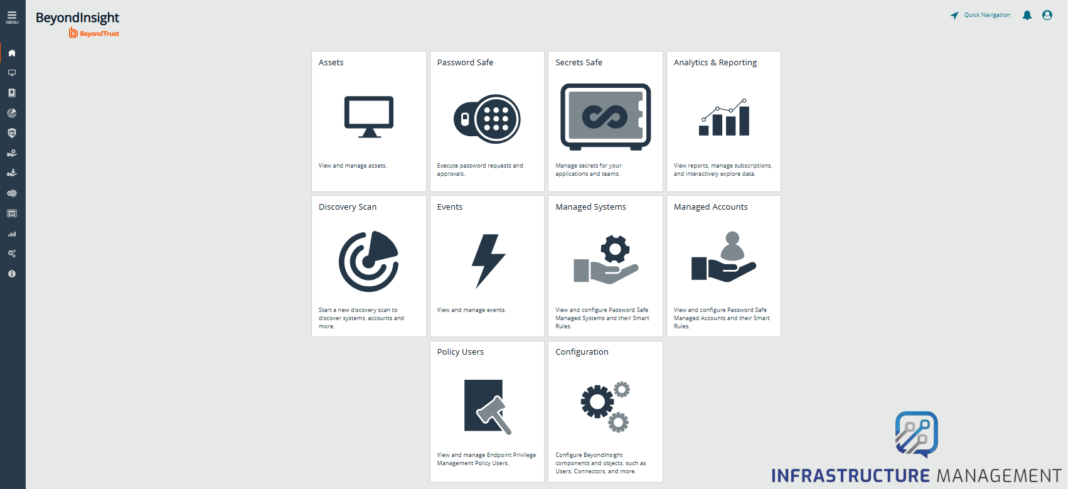
BeyondTrust Password Safe is a Privileged Access Management (PAM) solution used to secure privileged accounts, manage credentials, control access to systems, and monitor privileged sessions.
BeyondInsight provides a centralized console for managing and configuring the Password Safe environment.
1. BEYONDTRUST FUNDAMENTALS
– Understanding BeyondTrust Password Safe and BeyondInsight.
– Learning the purpose of Privileged Access Management.
– Understanding the relationship between managed systems and managed accounts.
2. SETUP AND CONFIGURATION
– Reviewing setup prerequisites and infrastructure requirements.
– Understanding the initial console setup.
– Reviewing user access, roles, and permissions.
– Learning about Active Directory integration.
3. ACCOUNT MANAGEMENT
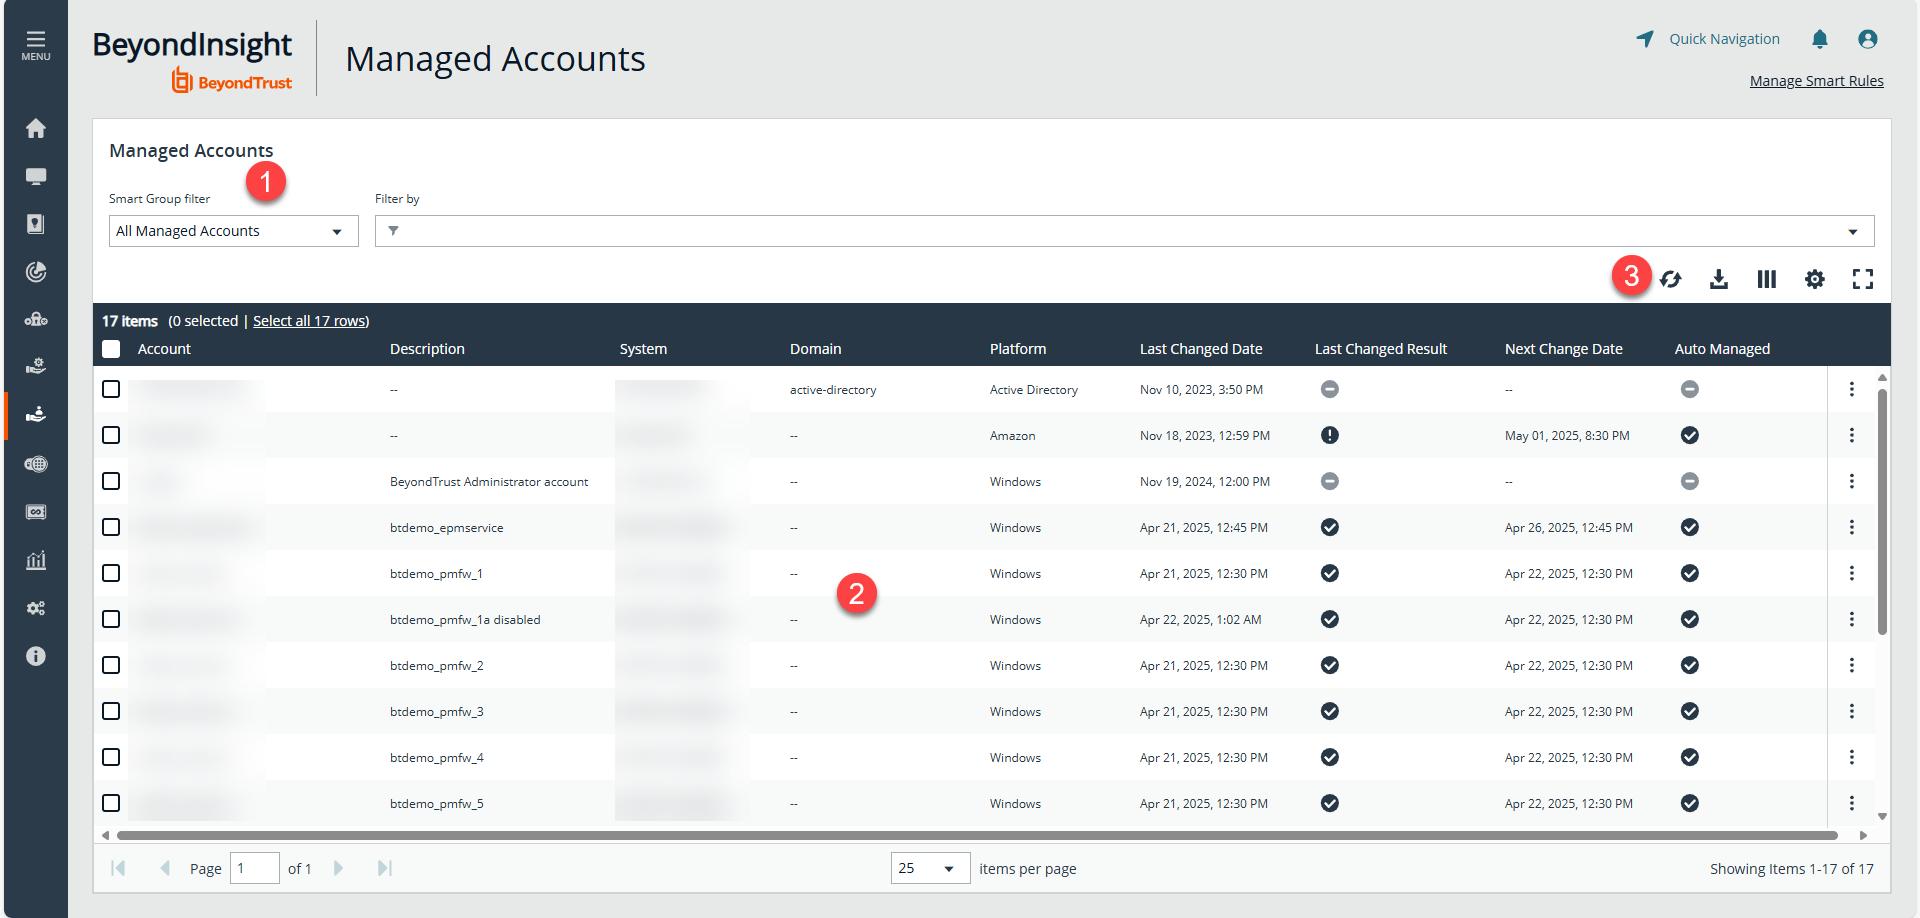
– Understanding bind, discovery, functional, and managed accounts.
– Learning the purpose of different accounts used during configuration.
– Reviewing account permissions and secure credential management.
4. ACTIVE DIRECTORY DISCOVERY
– Discovering Organizational Units (OUs) and computers.
– Working with directory queries.
– Reviewing discovery results and identifying assets for onboarding.
5. SMART RULES
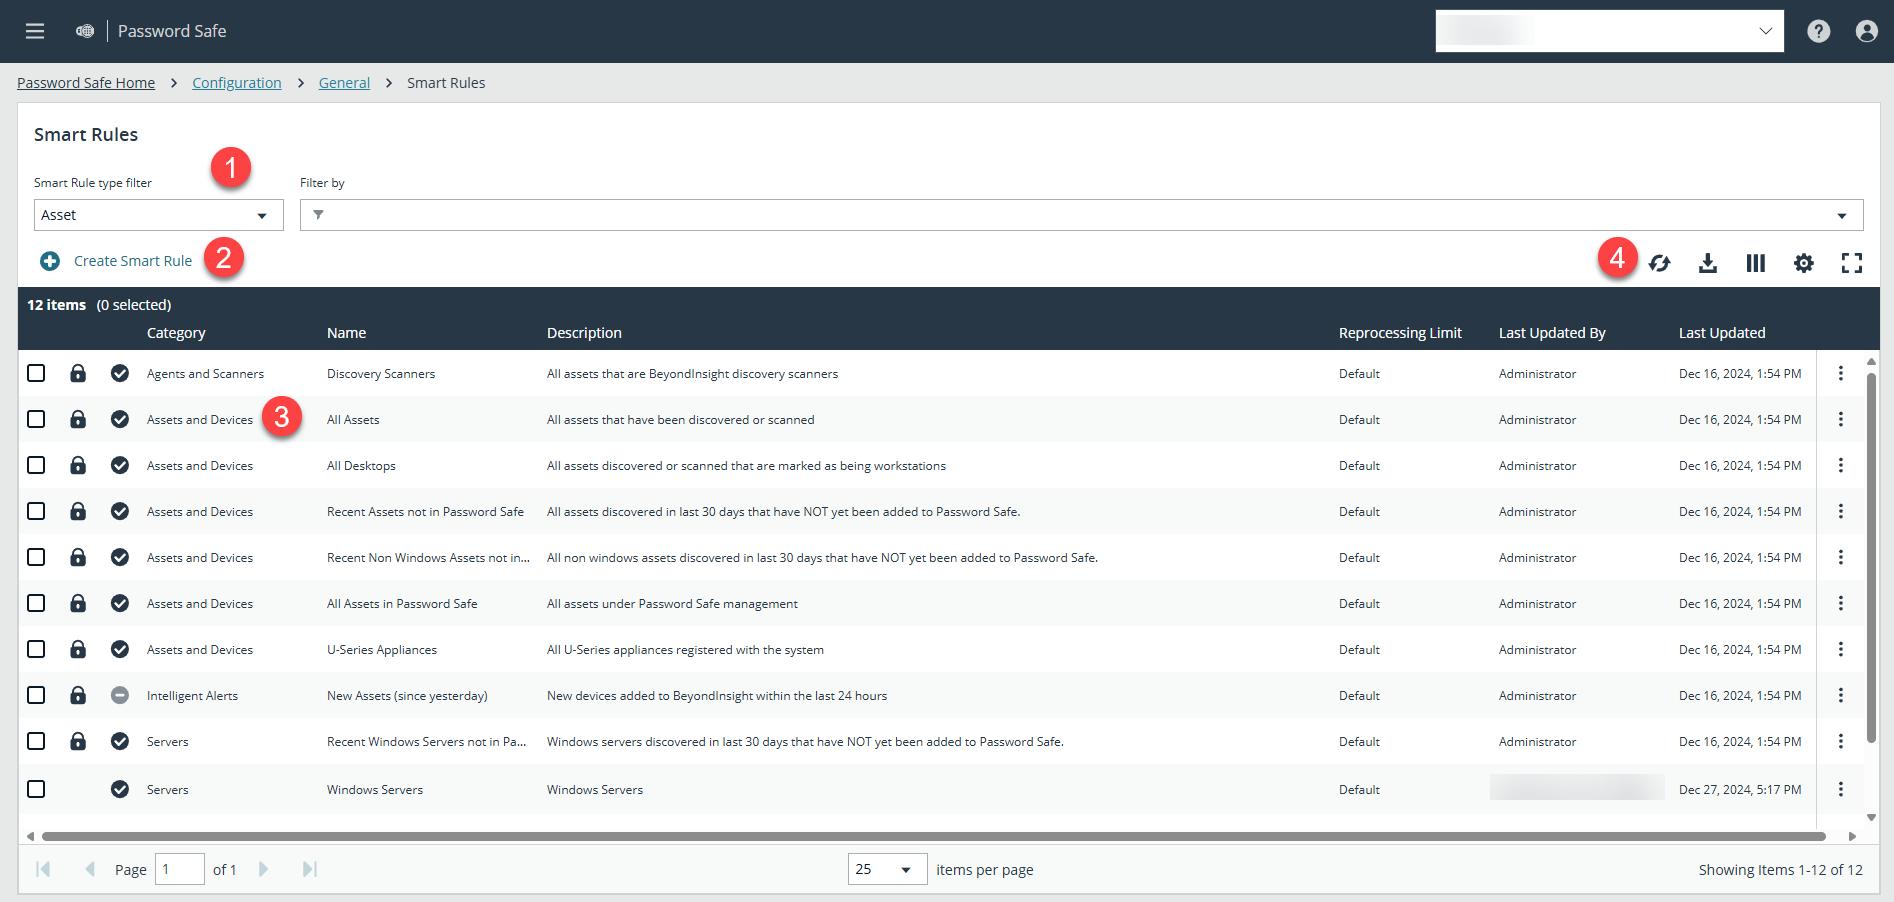
– Creating asset-based Smart Rules.
– Creating managed account-based Smart Rules.
– Understanding selection criteria and automated management actions.
6. SYSTEM AND ACCOUNT ONBOARDING
– Onboarding managed systems and accounts.
– Linking accounts to the correct systems.
– Reviewing account configuration and management status.
7. BACKUP AND SESSION MANAGEMENT
– Learning about backup and restore procedures.
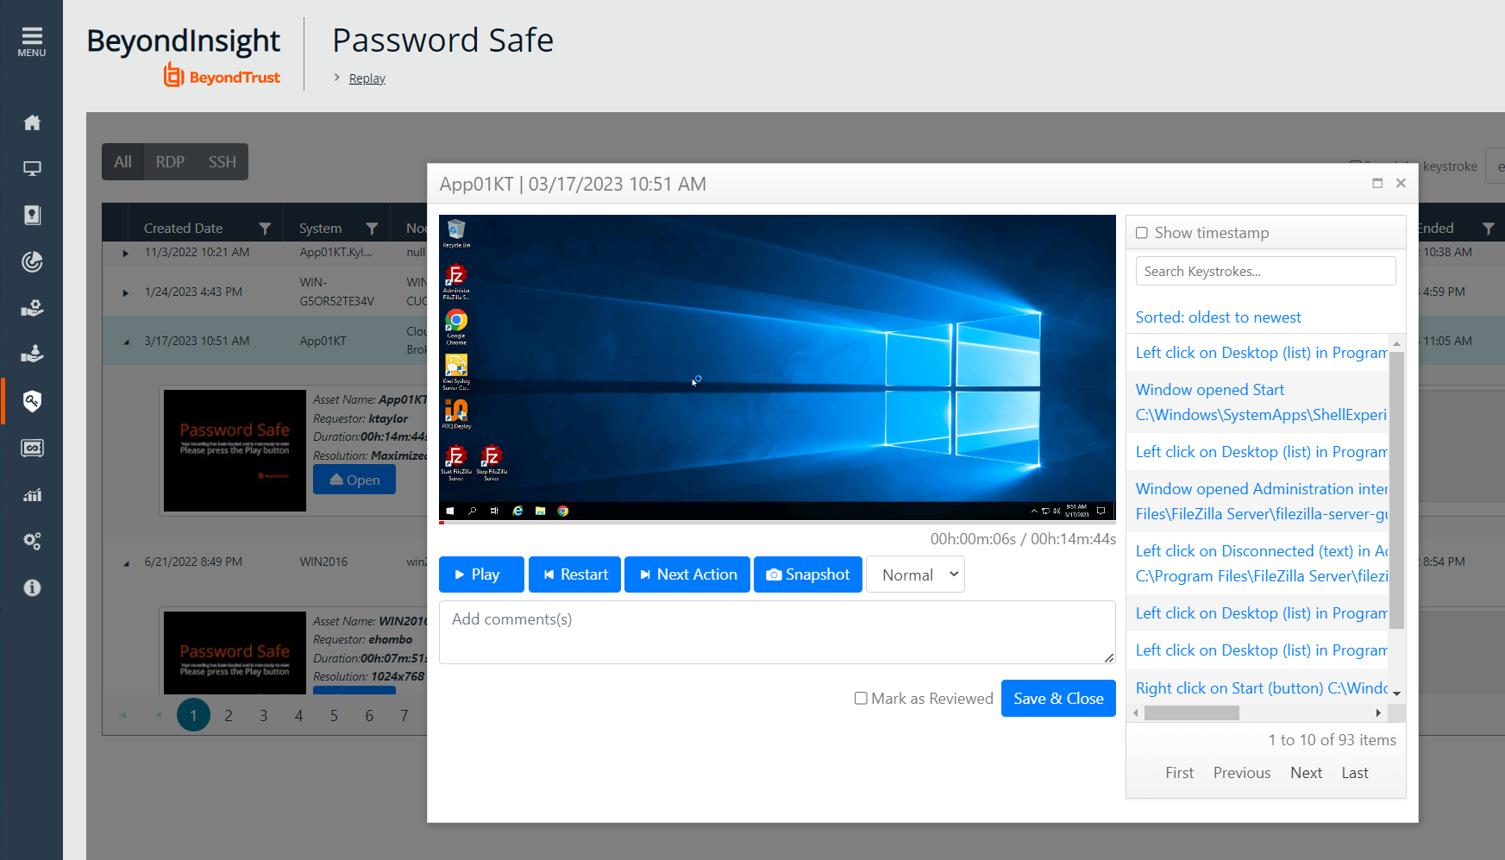
– Understanding session recording and archiving.
– Reviewing the importance of recovery validation and auditing.
8. BREAK-GLASS ACCESS
– Understanding emergency privileged access.
– Reviewing authorization, credential security, and audit requirements.
9. TESTING AND TROUBLESHOOTING
– Validating connectivity, permissions, and discovery results.
– Reviewing system and account onboarding issues.
– Understanding the importance of checking configuration and logs.
– Understood the main purpose of BeyondTrust Password Safe and BeyondInsight.
– Learned the roles of different accounts used in the PAM environment.
– Gained practical exposure to Active Directory discovery and Smart Rules.
– Learned system onboarding, account onboarding, and account-to-system mapping.
– Reviewed backup, session auditing, and emergency-access concepts.
– Understood the importance of least privilege, validation, and secure credential management.
The learning covered the core concepts and administration workflow of BeyondTrust Password Safe, including configuration, Active Directory discovery, Smart Rules, account onboarding, and security management. These topics provide a foundation for further learning and practical experience in Privileged Access Management.
Official BeyondTrust Documentation